Volume 2, Issue 3 (In Progress)


In Progress
Citations: Crossref logo 0,   0   |   Viewed: 1663, Download: 539
Table of Contents

Free Access | Research Article | 25 September 2026
A Layered Security Framework Against Prompt Injection in RAG-Based Chatbots
ICCK Transactions on Information Security and Cryptography | Volume 2, Issue 3: 192-215, 2026 | DOI: 10.62762/TISC.2026.712476
Abstract
Prompt injection is ranked as the most critical vulnerability in large language model (LLM) deployments by the OWASP Top 10 for LLM Applications, yet existing defenses operate at isolated pipeline stages and remain incomplete. Input filters cannot inspect retrieved documents, while output monitors cannot prevent malicious payloads from reaching the model. Consequently, retrieval-augmented generation (RAG) chatbots remain vulnerable to indirect injection, where a poisoned knowledge-base document compromises every user whose query retrieves it. We present a three-layer framework that intercepts both direct and indirect prompt injection throughout the inference pipeline. Layer 1 screens user in... More >

Graphical Abstract
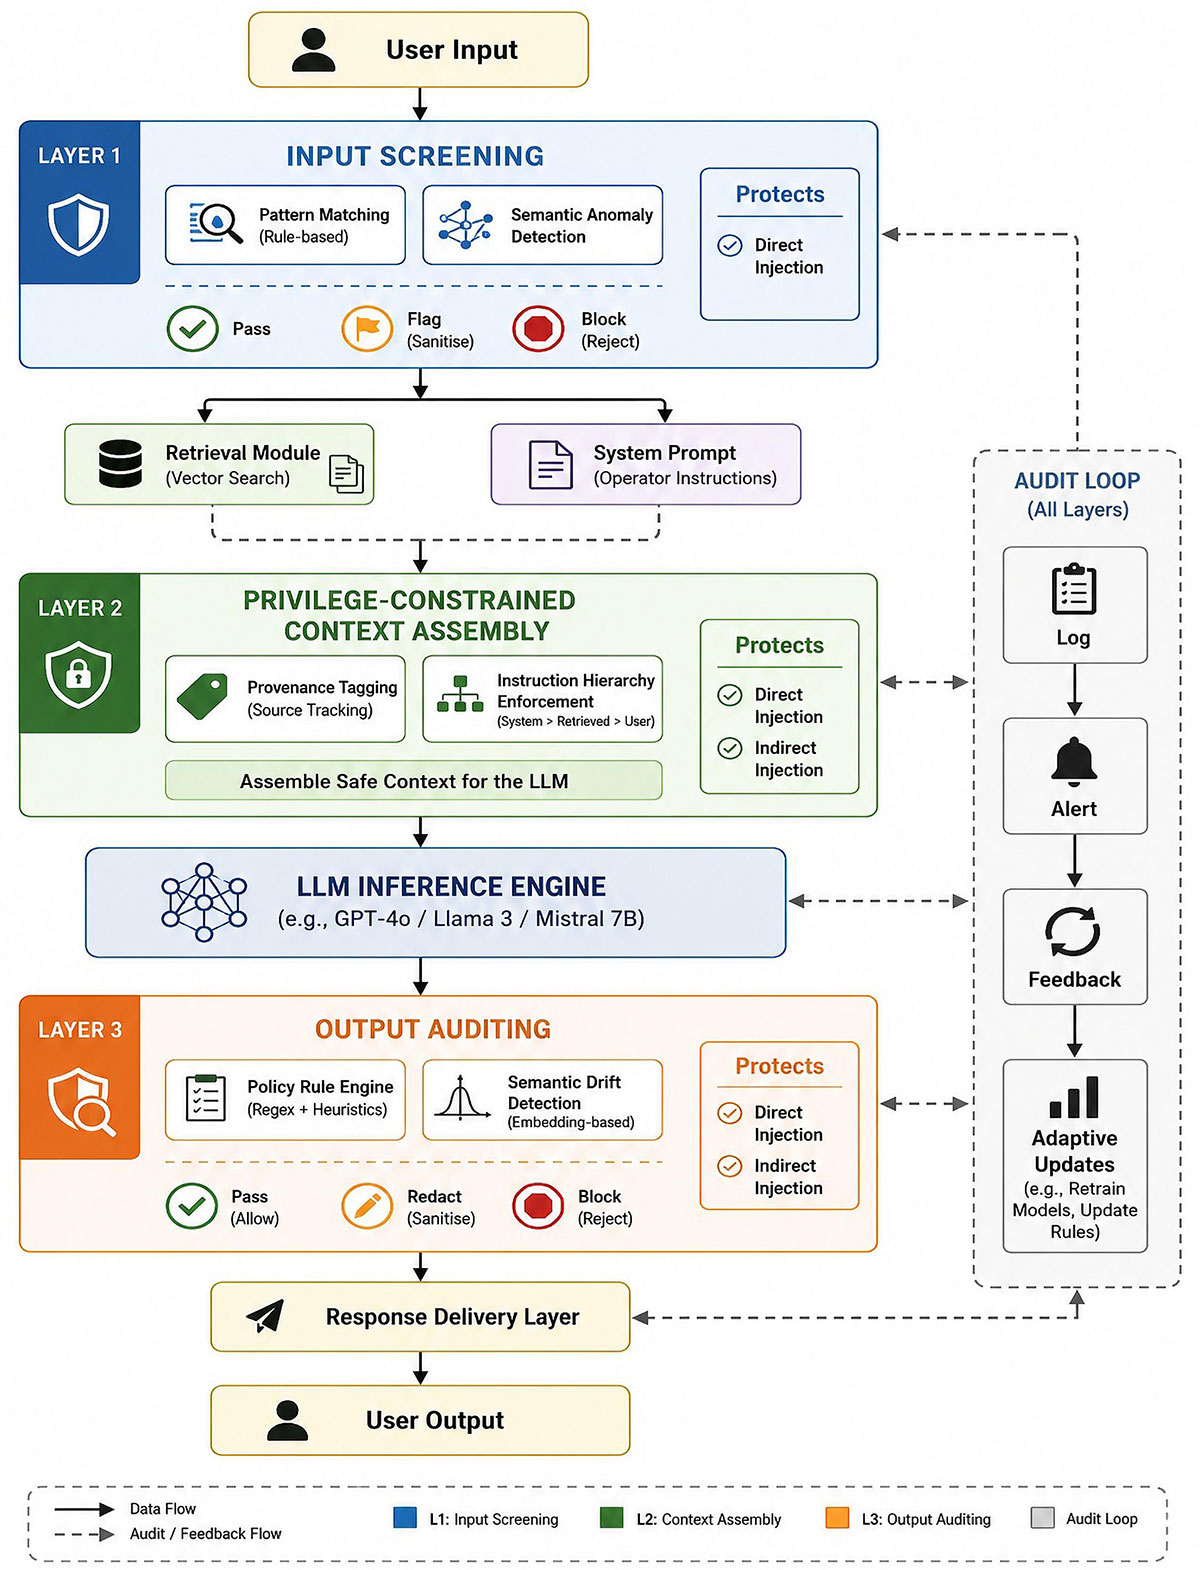
A Layered Security Framework Against Prompt Injection in RAG-Based Chatbots
Free Access | Research Article | 23 September 2026
A Secure and Auditable Distributed Data-Sharing Framework for Multi-Domain Systems
ICCK Transactions on Information Security and Cryptography | Volume 2, Issue 3: 172-191, 2026 | DOI: 10.62762/TISC.2026.917693
Abstract
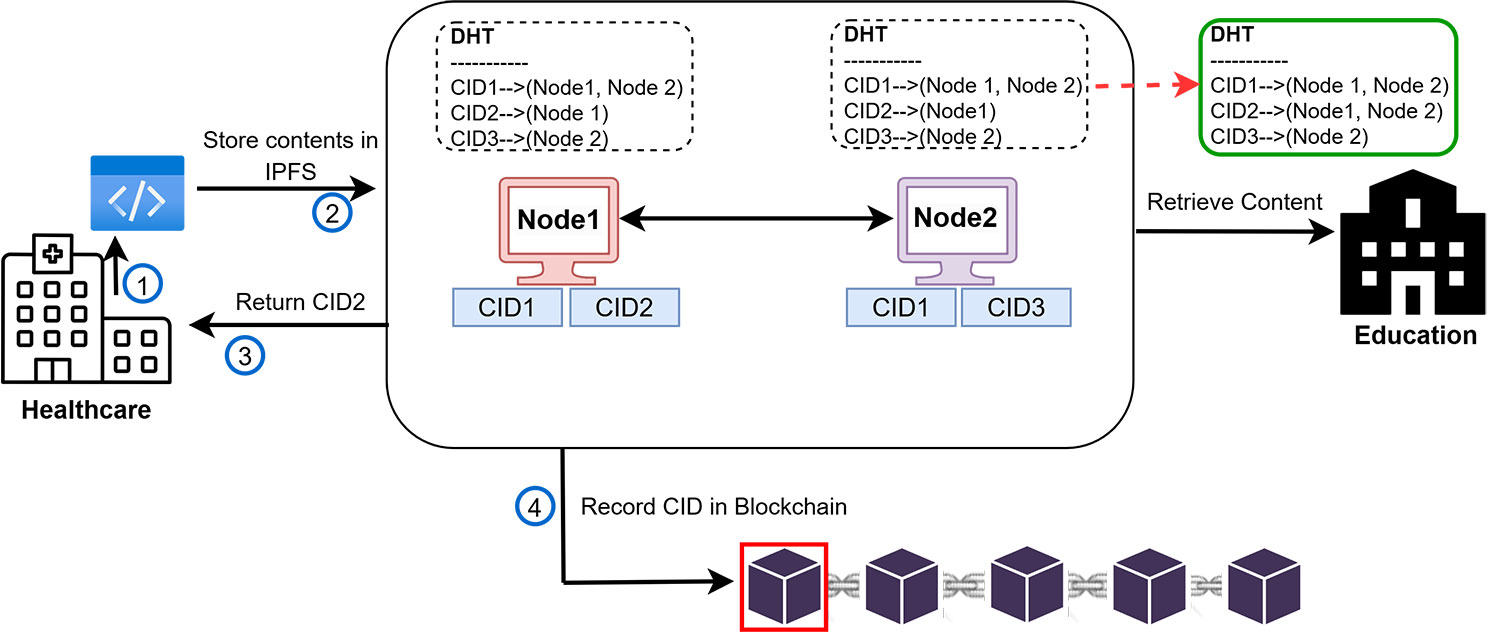
Data is one of the essential assets of every organisation, and its security has frequently been highlighted as a concern due to unauthorised access, breaches, and tampering. Conventional data repositories are often based on centralised setups, which are prone to problems such as single points of failure, privacy breaches, and unpredictable system behaviour. While an auditing mechanism can strengthen transparency by tracking how data is accessed, such tools are often managed by external third parties or rely on manual methods. Additionally, due to complexities such as duplicate user credentials across multiple services and systems, it becomes even more difficult for users to control their con... More >

Graphical Abstract
A Secure and Auditable Distributed Data-Sharing Framework for Multi-Domain Systems
Free Access | Research Article | 22 September 2026
Privacy-Preserving Machine Learning Using Homomorphic Encryption
ICCK Transactions on Information Security and Cryptography | Volume 2, Issue 3: 159-171, 2026 | DOI: 10.62762/TISC.2026.247194
Abstract
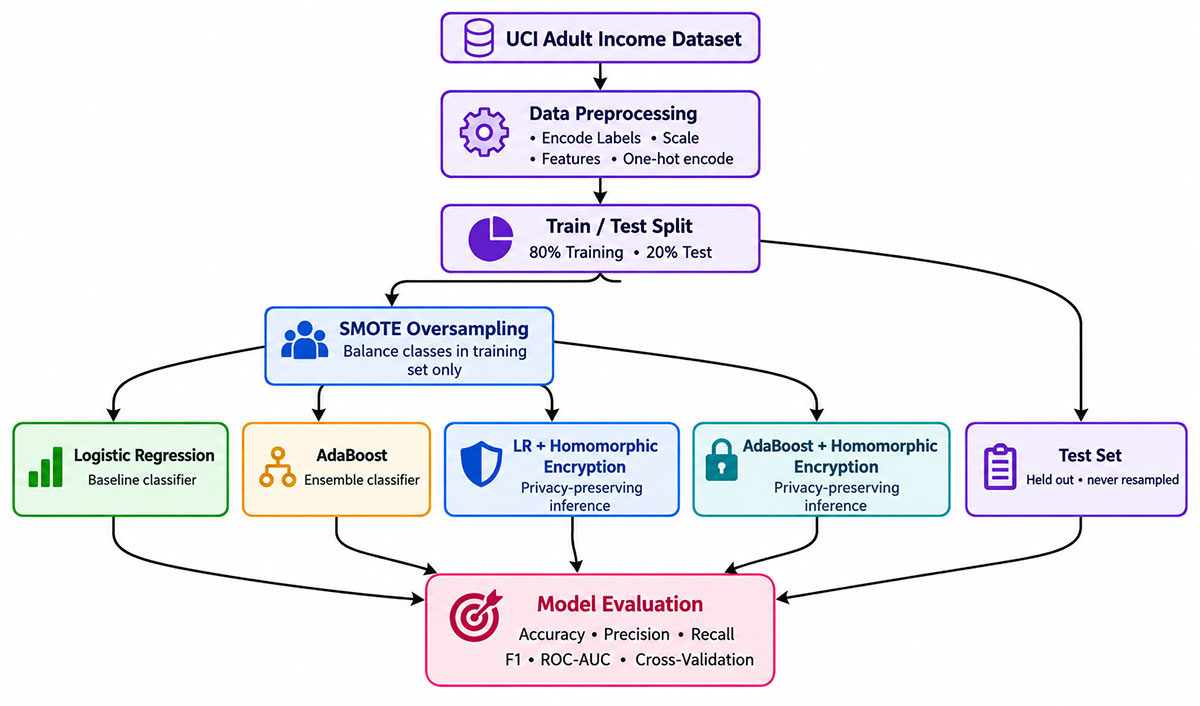
The exponential growth of machine learning applications in healthcare, finance, and cloud computing has raised significant data privacy concerns, as traditional encryption methods require access to decrypted data for processing, creating security vulnerabilities. Regulatory frameworks including the European Union's General Data Protection Regulation and the Health Insurance Portability and Accountability Act mandate privacy protection throughout the entire data management lifecycle. This research develops a privacy-preserving machine learning framework combining CKKS-based homomorphic encryption with Logistic Regression and AdaBoost classifiers using the UCI Adult Income dataset containing 4... More >

Graphical Abstract
Privacy-Preserving Machine Learning Using Homomorphic Encryption
Free Access | Review Article | 20 September 2026
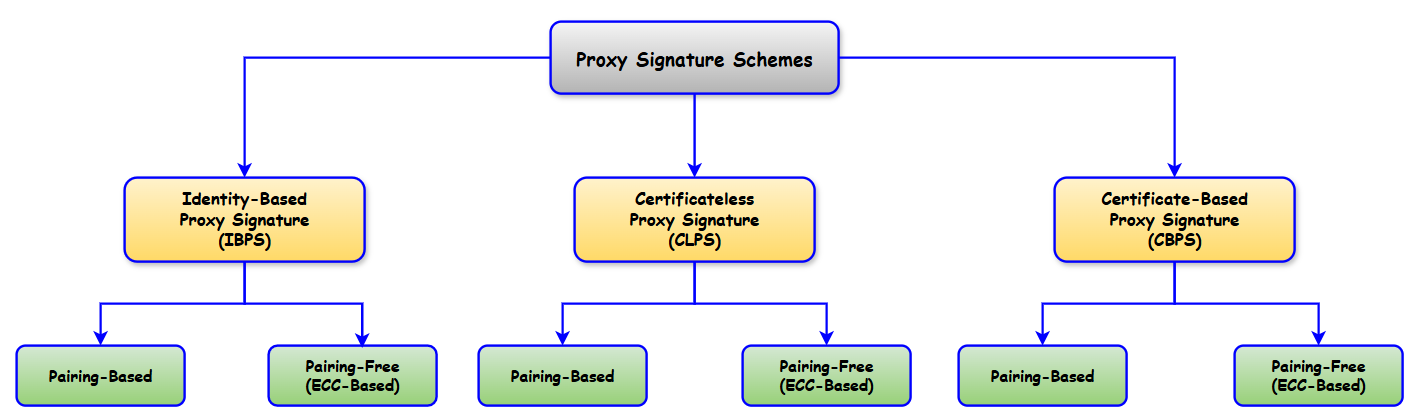
Security Vulnerabilities in Proxy Signature Schemes: Cryptanalysis, Design Weaknesses, and Open Challenges
ICCK Transactions on Information Security and Cryptography | Volume 2, Issue 3: 136-158, 2026 | DOI: 10.62762/TISC.2026.211619
Abstract
Proxy signature schemes allow an original signer to delegate signing authority to a proxy signer, supporting flexible authentication in distributed and resource-constrained environments such as cloud computing, blockchain, and Internet of Things (IoT) networks. Although many constructions have been proposed, a large number have later been broken due to flawed design assumptions, weak delegation binding, or the absence of rigorous provable security. This paper surveys proxy signature schemes with a focus on their security weaknesses. {It presents} a taxonomy of existing constructions by cryptographic primitive, delegation mechanism, and proof framework, {and then consolidates} known cryptanal... More >

Graphical Abstract
Security Vulnerabilities in Proxy Signature Schemes: Cryptanalysis, Design Weaknesses, and Open Challenges
Free Access | Research Article | 18 August 2026
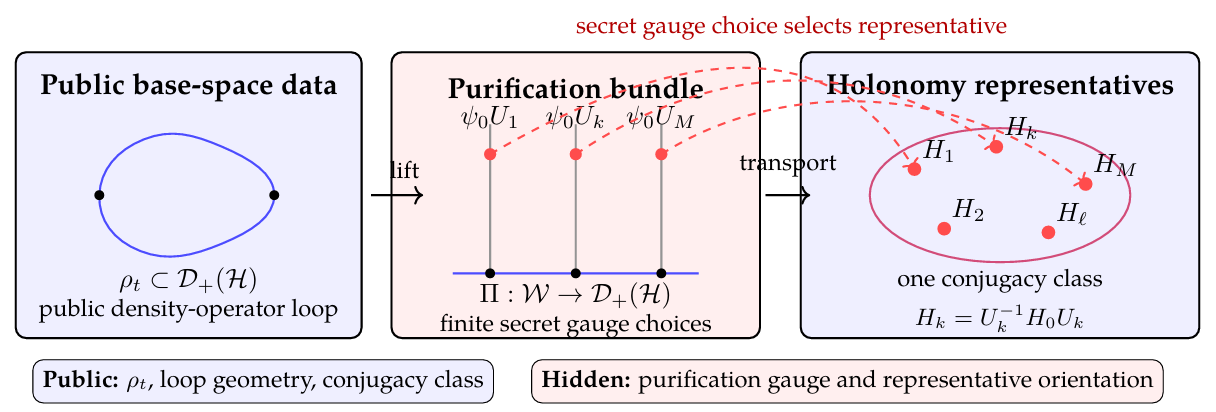
Discretized Holonomy as an Encoding Primitive for Quantum Cryptography
ICCK Transactions on Information Security and Cryptography | Volume 2, Issue 3: 119-135, 2026 | DOI: 10.62762/TISC.2026.243476
Abstract
Geometric phases in quantum systems give rise to holonomies associated with cyclic evolution. In mixed-state settings, these holonomies arise from Uhlmann parallel transport on the purification bundle of density operators and depend on the global geometry of density-operator trajectories. In this work we introduce discretized mixed-state holonomy as a geometric encoding primitive. The public object is a density-operator trajectory, while the encoded information resides in a finite family of purification gauges associated with the same holonomy conjugacy class. By discretizing the gauge freedom of the purification bundle, continuous mixed-state holonomy is converted into finite alphabets suit... More >

Graphical Abstract
Discretized Holonomy as an Encoding Primitive for Quantum Cryptography