Journal of Reliable and Secure Computing

Publishing Model:
ISSN:
ISSN: 3070-6424
The Journal of Reliable and Secure Computing (JRSC) is an international peer-reviewed journal dedicated to advancing research and practice in reliable, trustworthy, and secure computing.
DOI Prefix: 10.62762/JRSC

Journal Metrics

-
Impact Factor
-
CiteScore

Recent Articles

Open Access | Review Article | 17 June 2026 | Cited: Crossref logo  1
A Comprehensive Survey on Robustness and Privacy in Federated Learning Meets Large Language Model at Edge
Journal of Reliable and Secure Computing | Volume 2, Issue 2: 111-155, 2026 | DOI: 10.62762/JRSC.2026.942513
Abstract
Large Language Models (LLMs) have revolutionized natural language processing, yet their deployment is hindered by data, computation, and privacy constraints. Federated Learning (FL) offers a promising solution by enabling collaborative, privacy-preserving training across distributed devices, while the push for low-latency on-device intelligence further drives LLM integration into FL and edge settings—posing new challenges in heterogeneity and resource limits. This survey comprehensively reviews the integration of LLMs with federated learning, termed FLM, and its deployment at the edge, with particular emphasis on the robustness, privacy, and trustworthiness challenges that emerge across th... More >

Graphical Abstract
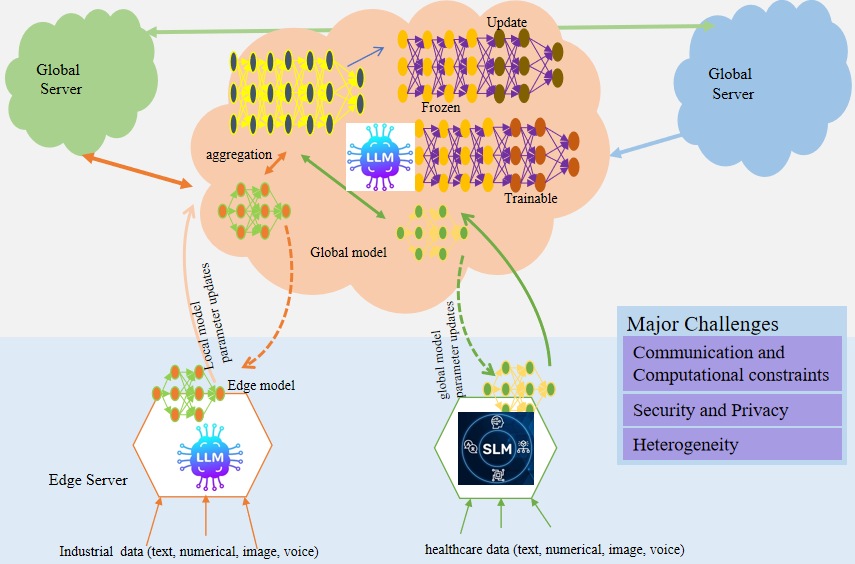
A Comprehensive Survey on Robustness and Privacy in Federated Learning Meets Large Language Model at Edge
Open Access | Research Article | 14 June 2026
Cryptanalysis of an Authentication Protocol for Edge-Centric Maritime Transportation Systems
Journal of Reliable and Secure Computing | Volume 2, Issue 2: 104-110, 2026 | DOI: 10.62762/JRSC.2026.765456
Abstract
With the rapid development of edge computing and intelligent maritime transportation systems, secure authentication and key agreement protocols have become essential for protecting communications among maritime entities and edge devices. Recently, Mahmood et al. proposed an authentication protocol for edge-centric maritime transportation systems, claiming that their scheme can resist various security attacks while ensuring efficient communication. However, practical maritime environments still face many security threats. In addition, edge infrastructures usually have limited resources. Therefore, authentication protocols require rigorous security evaluation. In this paper, we perform a crypt... More >
Open Access | Research Article | 31 May 2026
Energy-Optimized Blockchain Architectures for Sustainable Distributed Computing
Journal of Reliable and Secure Computing | Volume 2, Issue 2: 83-103, 2026 | DOI: 10.62762/JRSC.2026.157158
Abstract
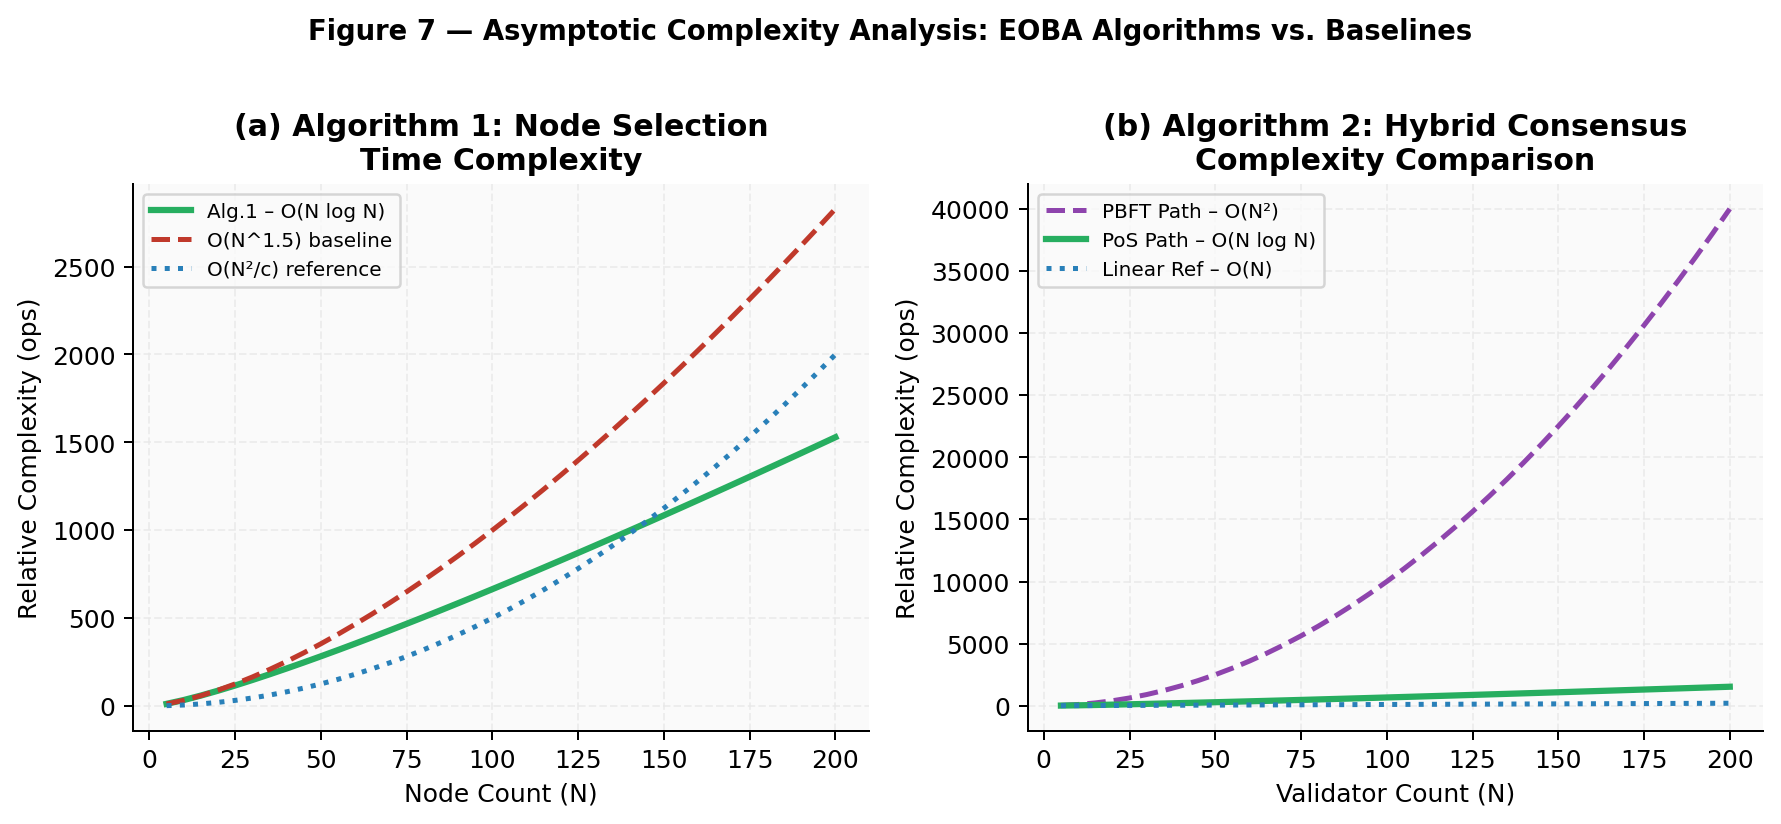
Blockchain technology offers transformative potential across distributed computing domains; however, dominant consensus mechanisms such as Proof of Work (PoW) impose severe energy and carbon costs, and existing research addresses only isolated components—consensus, storage, or sharding—rather than the full architectural system. This paper introduces the Energy-Optimized Blockchain Architecture (EOBA), the first nine-layer framework in which energy awareness is a foundational, cross-cutting design principle embedded across all architectural layers. EOBA integrates energy monitoring, hybrid energy-aware consensus, energy-guided task scheduling, dynamic sharding, hybrid on-chain/off-chain s... More >

Graphical Abstract
Energy-Optimized Blockchain Architectures for Sustainable Distributed Computing
Open Access | Research Article | 30 March 2026 | Cited: Crossref logo  1 , Scopus 2
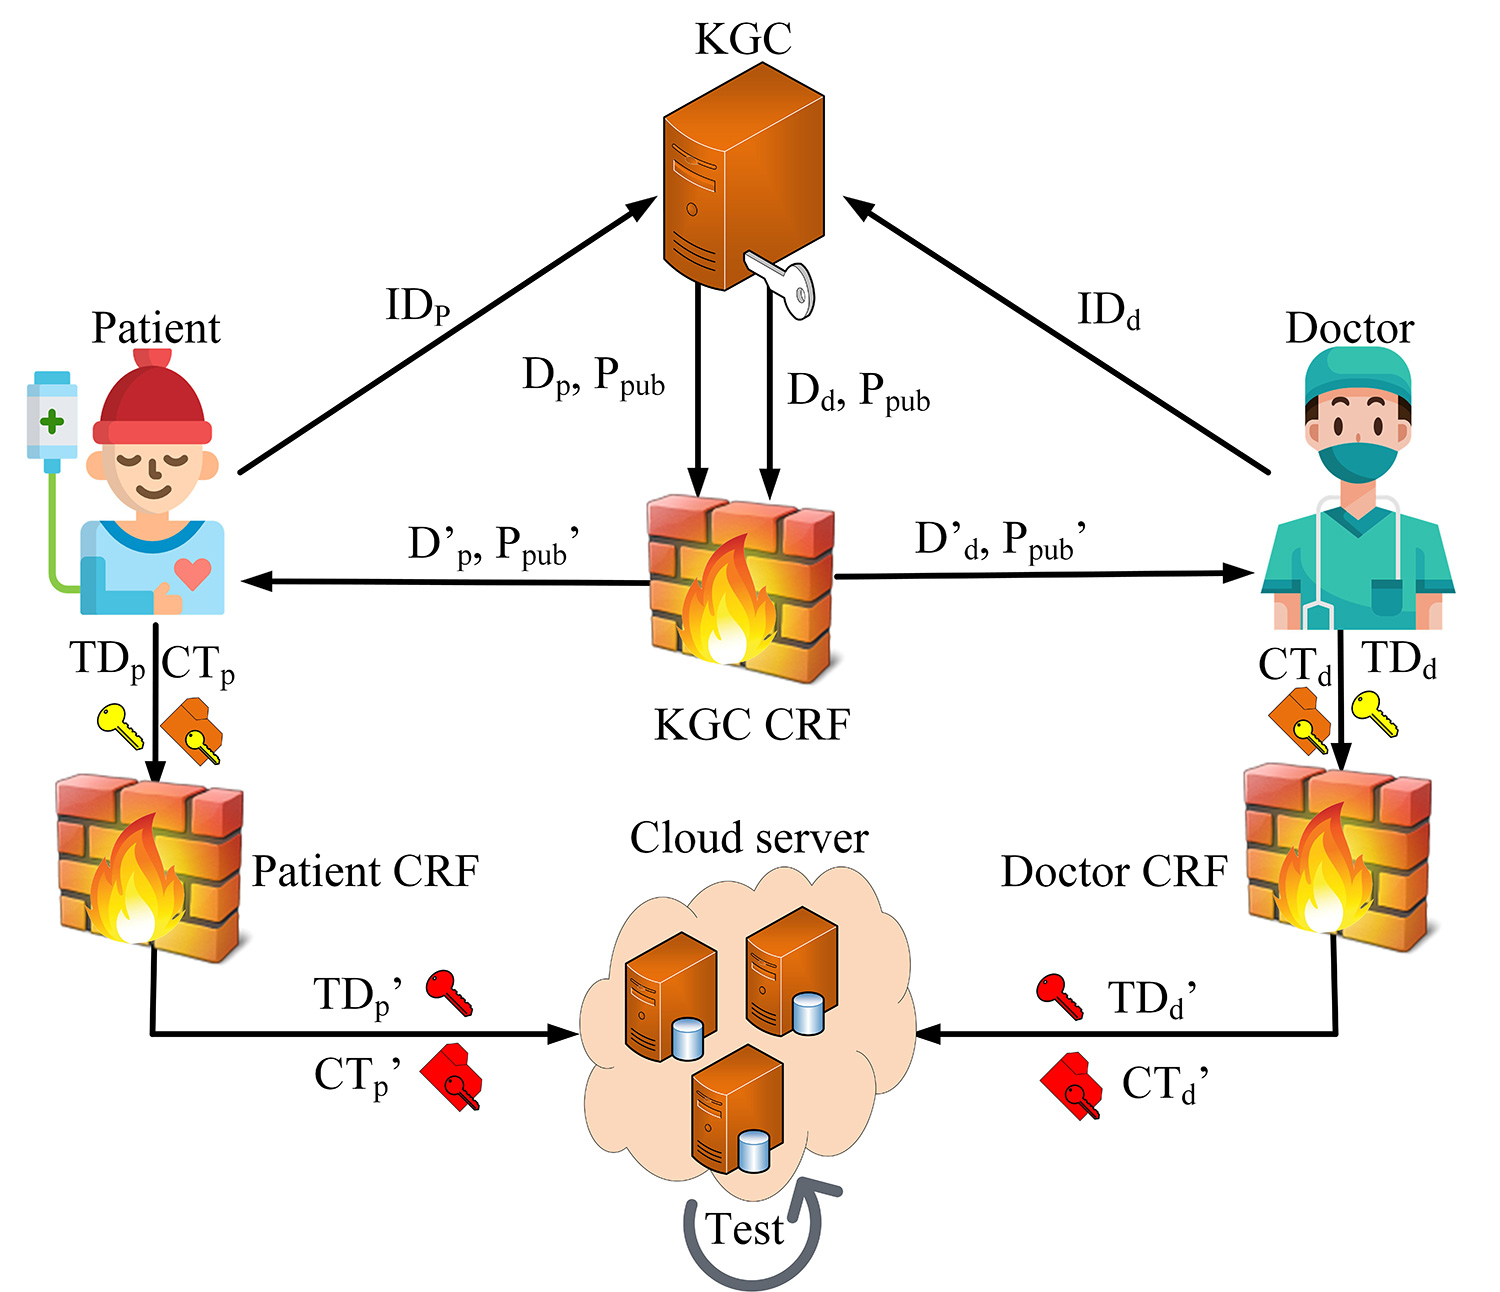
Certificateless Encryption Supporting Equality Test with Cryptographic Reverse Firewalls in Smart City
Journal of Reliable and Secure Computing | Volume 2, Issue 1: 66-82, 2026 | DOI: 10.62762/JRSC.2025.581803
Abstract
In the context of smart cities, sensors are pivotal for the collection and analysis of health data within smart healthcare systems. Despite their importance, securing this data for cloud storage poses significant challenges, particularly in terms of data searchability and encryption. Our paper introduces a novel solution, namely certificateless encryption supporting equality test with cryptographic reverse firewalls (CLE-ET-CRF). This protocol allows cloud servers to perform equality tests on encrypted data without compromising its confidentiality, effectively mitigating risks like offline message recovery attacks (OMRA) and algorithm substitution attacks (ASAs). By eliminating the need for... More >

Graphical Abstract
Certificateless Encryption Supporting Equality Test with Cryptographic Reverse Firewalls in Smart City
Open Access | Research Article | 27 March 2026 | Cited: Crossref logo  2 , Scopus 3
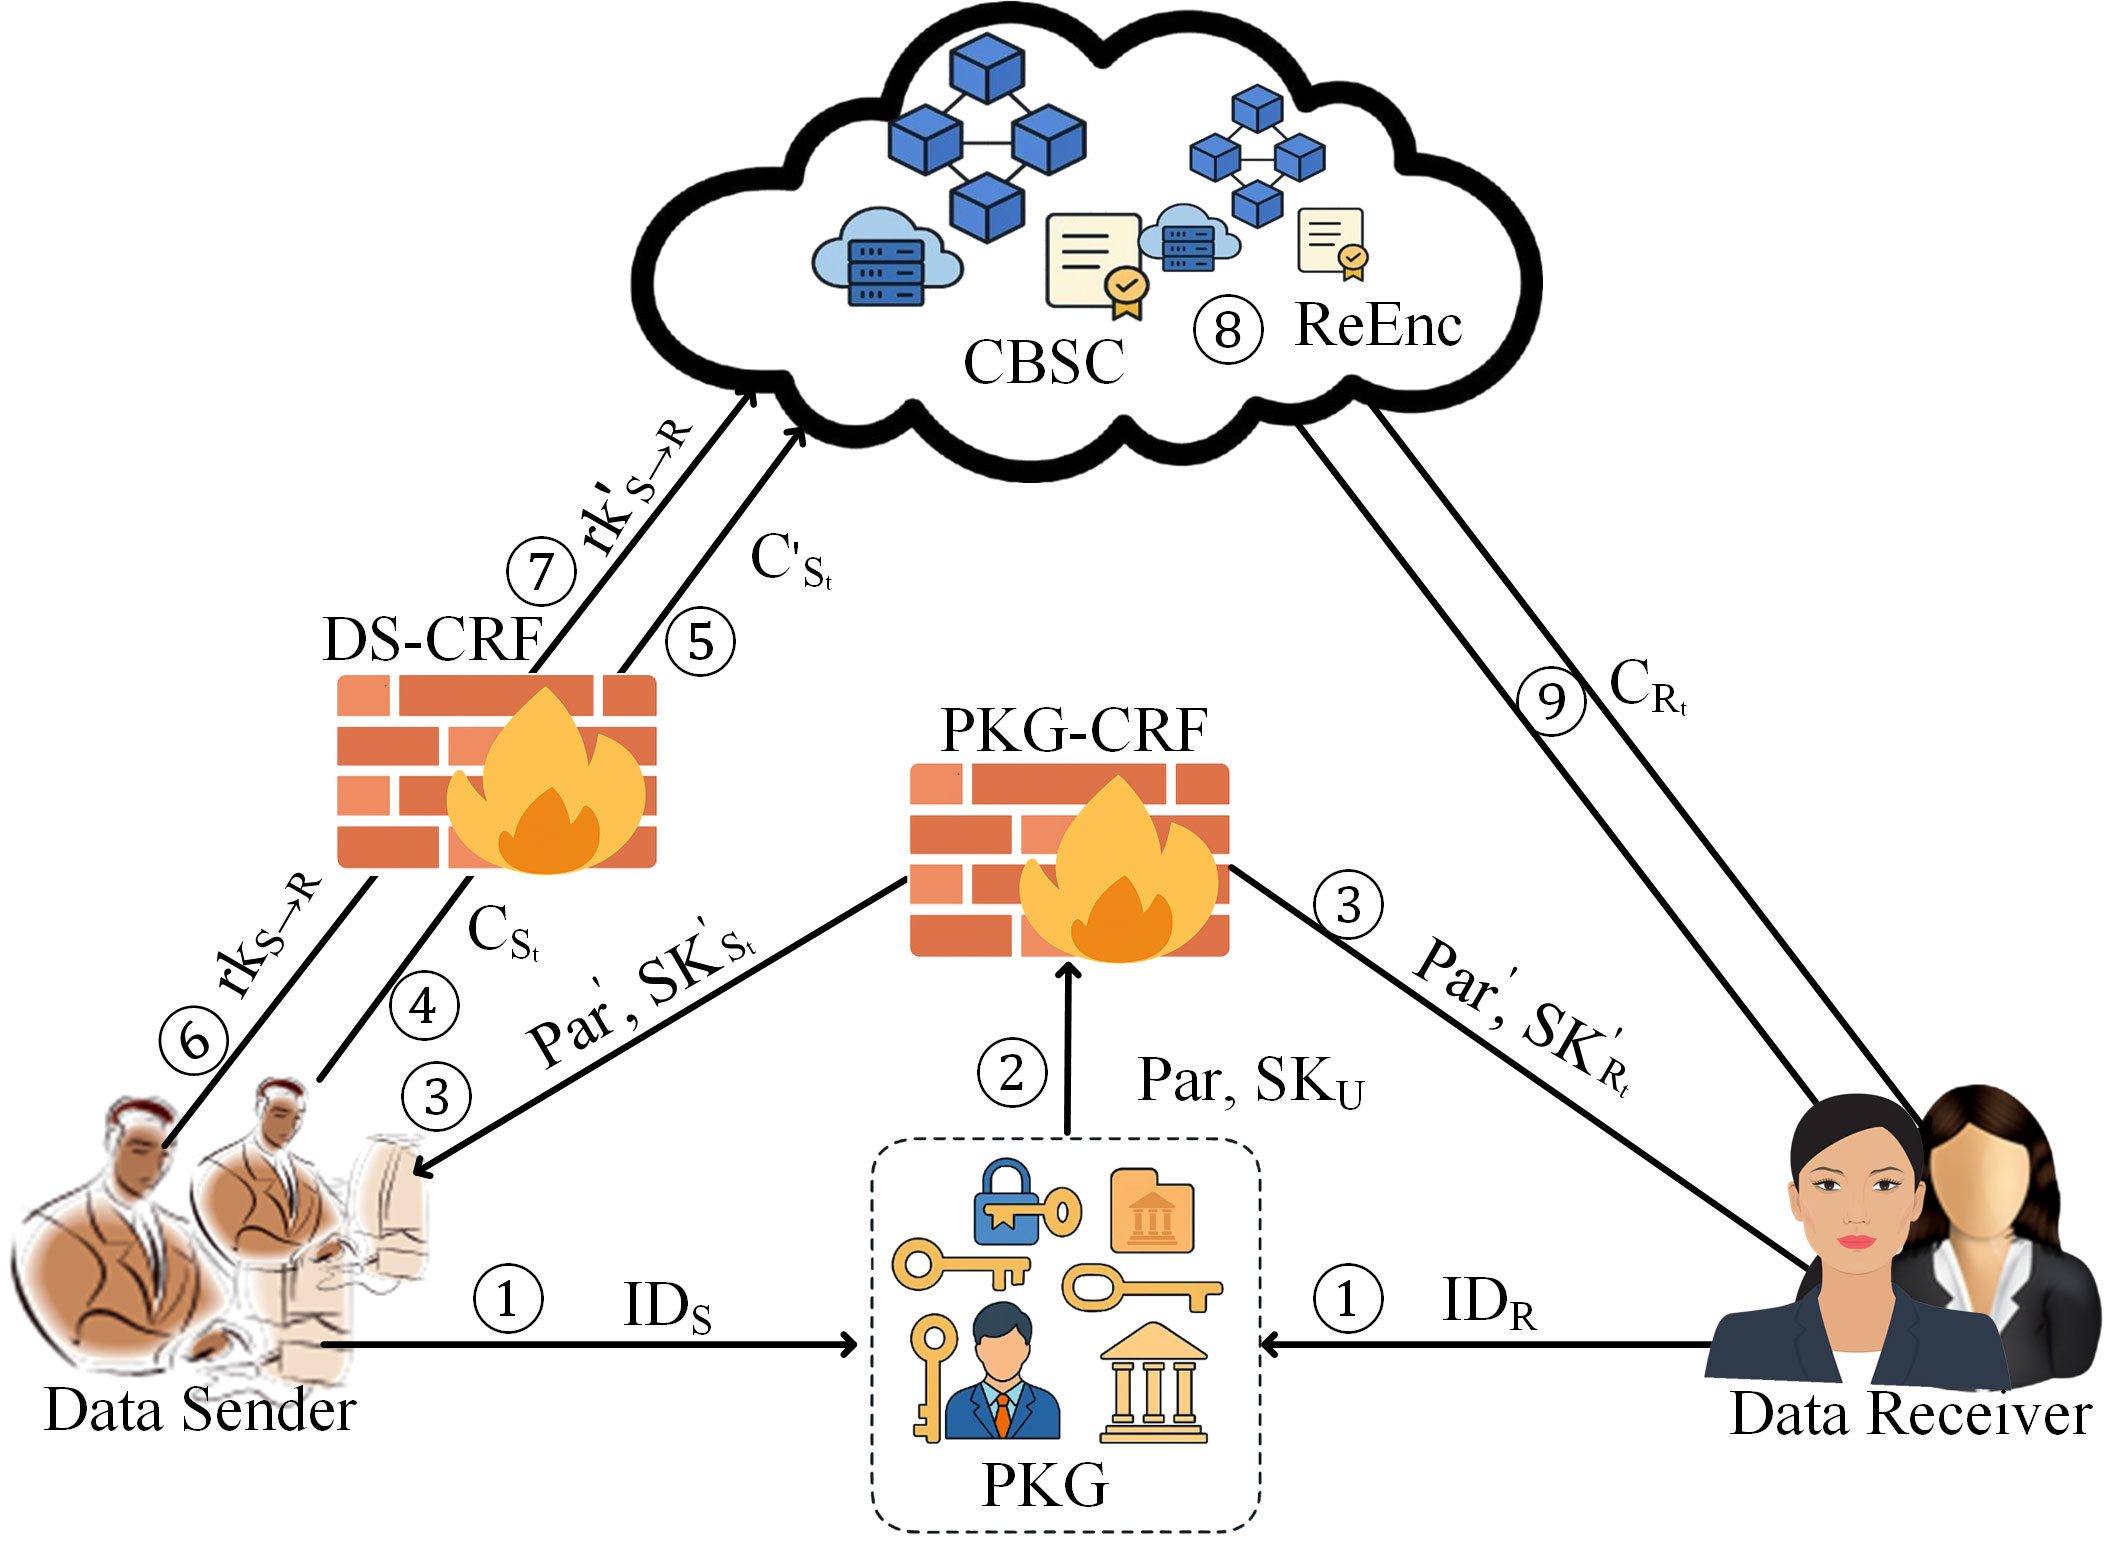
A Blockchain-Based Revocable Identity-Based Proxy Re-Encryption Scheme with Cryptographic Reverse Firewalls for Secure Data Sharing
Journal of Reliable and Secure Computing | Volume 2, Issue 1: 50-65, 2026 | DOI: 10.62762/JRSC.2026.796877
Abstract
With the rapid growth of Internet of Things (IoT) applications and decentralized data-driven systems, secure and flexible data sharing remains a critical challenge. Identity-Based Proxy Re-Encryption (IB-PRE) is an effective cryptographic primitive for enabling fine-grained access delegation without exposing plaintext data. However, existing IB-PRE schemes remain vulnerable to algorithm substitution attacks (ASA), malicious key generation, inefficient ciphertext management, and the lack of practical revocation mechanisms. To address these limitations, we propose a blockchain-based revocable identity-based proxy re-encryption scheme with cryptographic reverse firewalls (BRIBPR-CRF) for secure... More >

Graphical Abstract
A Blockchain-Based Revocable Identity-Based Proxy Re-Encryption Scheme with Cryptographic Reverse Firewalls for Secure Data Sharing
Open Access | Research Article | 24 March 2026 | Cited: Crossref logo  3 , Scopus 6
A Conditional Privacy-Preserving Short Signature Scheme for Industrial Internet of Things
Journal of Reliable and Secure Computing | Volume 2, Issue 1: 39-49, 2026 | DOI: 10.62762/JRSC.2026.376190
Abstract
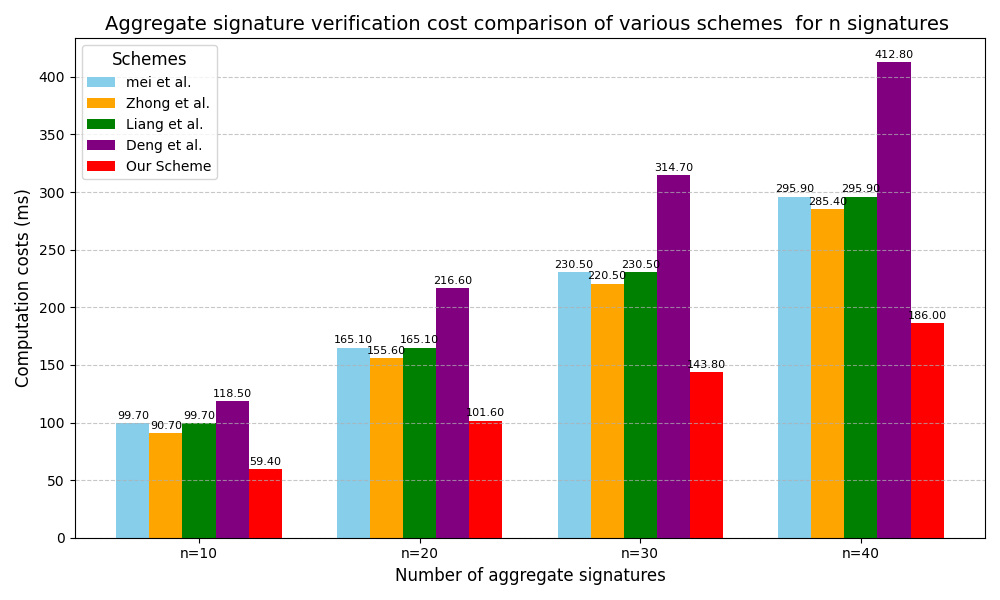
Securely transmitting a large amount of data in a short time is a serious challenge in today's digital age. Cryptographic primitives can significantly alleviate this problem. The invention of digital signatures represents a major advance in this area. The Certificateless Aggregate Signature (CLAS) scheme is a cryptographic primitive that greatly reduces the computation cost by aggregating several signatures into a single short signature. However, the costs of aggregate signatures have not been reduced to the desired extent. In this paper, we propose a certificateless aggregate signature scheme that requires only two bilinear pairing operations to verify both a single signature and an aggrega... More >

Graphical Abstract
A Conditional Privacy-Preserving Short Signature Scheme for Industrial Internet of Things
Open Access | Research Article | 07 February 2026 | Cited: Crossref logo  1 , Scopus 1
A Novel System for Detecting Model Poisoning Attacks in Federated Learning
Journal of Reliable and Secure Computing | Volume 2, Issue 1: 27-38, 2026 | DOI: 10.62762/JRSC.2025.385825
Abstract
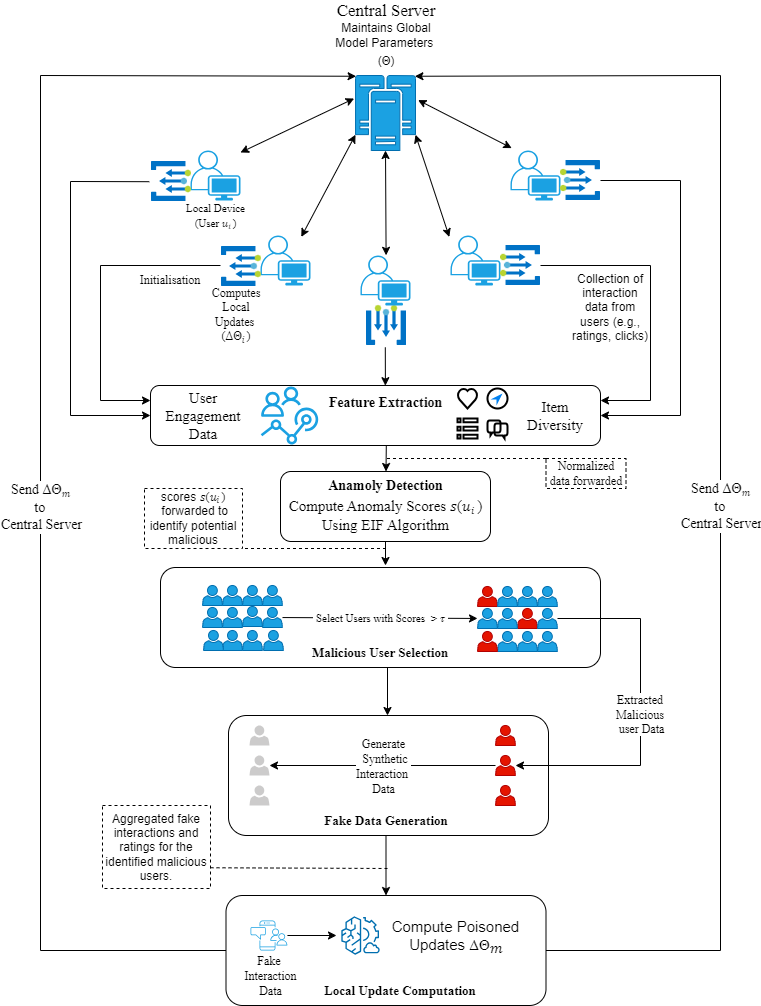
Federated learning (FL) enables decentralized model training and enhances user privacy by keeping data on local devices. Despite these advantages, FL remains vulnerable to sophisticated adversarial attacks. Federated recommender systems (FRS), an important application of FL, are particularly susceptible to threats such as model poisoning. In this paper, we propose DyMUSA, a novel model poisoning attack tailored for FRS. DyMUSA exploits systemic vulnerabilities through dynamic user selection and adaptive poisoning strategies. Specifically, it leverages the Isolation Forest algorithm to identify anomalous users and generate poisoned gradients that compromise the integrity of the recommender sy... More >

Graphical Abstract
A Novel System for Detecting Model Poisoning Attacks in Federated Learning
Open Access | Research Article | 28 January 2026 | Cited: Crossref logo  4 , Scopus 4
Blockchain Consensus Mechanisms and Enhancement Techniques for Federated Learning-Based Intrusion Detection Systems in IoT Smart Homes
Journal of Reliable and Secure Computing | Volume 2, Issue 1: 1-26, 2026 | DOI: 10.62762/JRSC.2025.761390
Abstract
The rapid proliferation of smart home IoT devices has introduced unprecedented cybersecurity vulnerabilities, necessitating scalable and privacy-preserving intrusion detection systems (IDS). Federated Learning (FL) offers a promising decentralized approach by training models locally without sharing raw data, but it remains susceptible to poisoning attacks and relies on a vulnerable central aggregator. This paper presents a novel blockchain-enhanced FL framework tailored for smart home IDS, integrating multiple consensus mechanisms—Proof-of-Stake (PoS), Practical Byzantine Fault Tolerance (PBFT), and Proof-of-Authority (PoA)—for the first time in this context. Our approach uniquely combin... More >

Graphical Abstract
Blockchain Consensus Mechanisms and Enhancement Techniques for Federated Learning-Based Intrusion Detection Systems in IoT Smart Homes

Journal Statistics

54
Authors
16
Countries / Regions
21
Articles
37
Scopus Citations
38.1% Cited
2025
Published Since
46,256
Article Views
11,689
Article Downloads
Journal of Reliable and Secure Computing
eISSN: 3070-6424
Crossref
Crossref
Member of Crossref
Visit Crossref →